.png)
 4 days ago
12
Article content
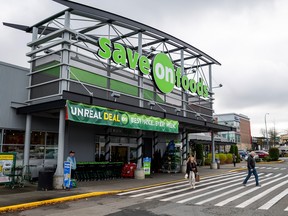
Thousands of customers of Save-On-Foods have received news their personal information had been accessed when the supermarket’s servers were breached by hackers earlier this week.
THIS CONTENT IS RESERVED FOR SUBSCRIBERS ONLY
Subscribe now to read the latest news in your city and across Canada.
- Unlimited online access to articles from across Canada with one account.
- Get exclusive access to the Vancouver Sun ePaper, an electronic replica of the print edition that you can share, download and comment on.
- Enjoy insights and behind-the-scenes analysis from our award-winning journalists.
- Support local journalists and the next generation of journalists.
- Daily puzzles including the New York Times Crossword.
SUBSCRIBE TO UNLOCK MORE ARTICLES
Subscribe now to read the latest news in your city and across Canada.
- Unlimited online access to articles from across Canada with one account.
- Get exclusive access to the Vancouver Sun ePaper, an electronic replica of the print edition that you can share, download and comment on.
- Enjoy insights and behind-the-scenes analysis from our award-winning journalists.
- Support local journalists and the next generation of journalists.
- Daily puzzles including the New York Times Crossword.
REGISTER / SIGN IN TO UNLOCK MORE ARTICLES
Create an account or sign in to continue with your reading experience.
- Access articles from across Canada with one account.
- Share your thoughts and join the conversation in the comments.
- Enjoy additional articles per month.
- Get email updates from your favourite authors.
THIS ARTICLE IS FREE TO READ REGISTER TO UNLOCK.
Create an account or sign in to continue with your reading experience.
- Access articles from across Canada with one account
- Share your thoughts and join the conversation in the comments
- Enjoy additional articles per month
- Get email updates from your favourite authors
Sign In or Create an Account
or
Article content
The company, part of the Pattison Food Group that includes Buy-Low Foods, Choices Markets, Nature’s Fare Markets, Nesters Market, and Urban Fare, said it detected unauthorized activity in a server containing information of its rewards system on Tuesday.
Article content
Article content
Advertisement 1
Article content
“(We) took immediate action that day to shut down the server and launch an investigation with a third-party cybersecurity expert. The incident was quickly contained, and we are in the process of notifying the appropriate authorities and privacy regulators,” said an email sent to affected customers on Friday night.
Article content
By signing up you consent to receive the above newsletter from Postmedia Network Inc.
Article content
“We have today confirmed that your name, and, if provided, address, phone number, email addresses and date of birth on the More Rewards database were accessed during this incident.
Article content
” … We take our responsibility to protect personal information seriously and regret any inconvenience this may cause.”
Article content
When contacted for further information on Saturday, the company replied by forwarding the body of the email sent to customers on Friday.
Article content
A spokesperson wrote, “according to the information available” no other personal information — like passwords, credit card data, or transaction history — was accessed during the breach, and reiterated that they won’t contact a customer to request sensitive information like verification codes, banking or payment card information, Social Insurance Number, or security question answers.
Article content
Advertisement 2
Article content
“If you receive communication that appears to be from us or anyone else requesting sensitive personal information or asking you to click on a link or open an attachment that you were not expecting, we encourage you to verify the request using contact information you know to be legitimate, and not any contact information included in such request,” the email reads.
Article content
Article content
The company did not respond to questions as to the scope of the breach, how many customers had been affected, or if information like credit card numbers or transaction history could be potentially accessed through the affected severs.
Article content





 Bengali (BD) ·
 English (US) ·